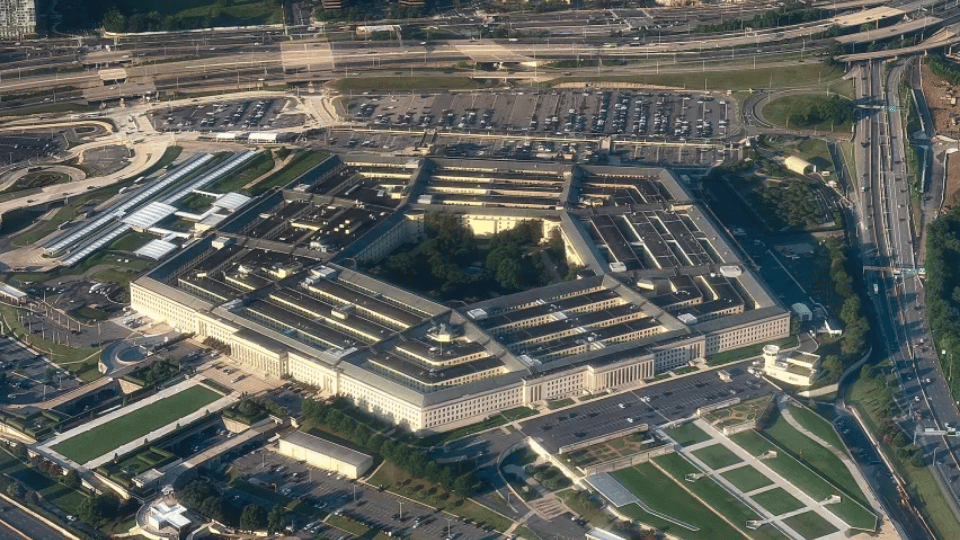
The United States government is notifying millions of current and former military personnel after hackers compromised Pentagon personnel files in a months-long data breach. Unauthorized intruders exploited a security vulnerability inside an unspecified file-sharing platform between October 2025 and mid-July 2026, systematically downloading sensitive records over several months.
An official breach notice issued by the Defense Manpower Data Center confirms that stolen files contained unencrypted personally identifiable information. The exposed files include full names, Social Security numbers, dates of birth, sex, race, and detailed military service histories. Defense Department officials state that the security breach impacts roughly 2.8 million living individuals and nearly 300,000 deceased military members.
While the Defense Manpower Data Center remains unfamiliar to most civilians, it serves as the primary record keeper for the Department of Defense. The agency maintains over 60 million active records for service members, military civilian staff, and their families, managing essential entitlements like healthcare, retirement benefits, and identification verification. The unit also acts as the primary identity manager for the armed forces, linking active credentials, passwords, and smart cards to secure computer systems, military bases, and restricted federal facilities.
Department of Defense officials claim they found no evidence showing that stolen personnel files have been misused, though spokespeople declined to explain how investigators reached that conclusion. The Pentagon incident represents the latest in a series of severe cyber attacks against federal agencies. Earlier this autumn, hackers associated with the ShinyHunters group compromised internal FBI applicant files, exposing sensitive details belonging to agents and staff members. Intelligence analysts warn that foreign intelligence agencies could use stolen personnel data to profile, target, or coerce federal workers holding security clearances.
The scale of the Pentagon intrusion mirrors previous massive cyber attacks against federal human resources databases. In 2015, a breach at the Office of Personnel Management exposed private files belonging to more than 22 million government workers, an attack widely attributed to state-sponsored Chinese hacking groups. Leaving millions of military records unencrypted inside exposed file-sharing systems highlights ongoing failures in federal network security.
Beyond the immediate risks of identity theft, leaking military service histories creates severe long-term national security vulnerabilities. Hostile intelligence services systematically index stolen personnel databases to build comprehensive profiles of active service members, intelligence officers, and specialized contractors holding high-level clearances. Cross-referencing military deployment records with external data leaks allows adversaries to track key defense personnel, uncover covered assignments, and identify potential targets for coercion or digital surveillance operations.
Failing to encrypt sensitive military files inside third-party file-sharing tools leaves millions of service members vulnerable to identity theft and foreign espionage. As cyber threat groups target federal identity databases, defense agencies must enforce strict encryption standards and continuous monitoring across all network portals. Protecting military personnel records requires continuous technical oversight, preventing unauthorized access before hackers extract critical national security data. The Defense Department must overhaul its identity management protocols and eliminate unencrypted storage solutions across all vendor networks to ensure that personnel data remains fully protected against future foreign cyber campaigns.